DR 01
Save normally
Save a file to FRAGGLEdrive™ the same way you'd save to any drive. No new export step, no retraining or learning, no change to the workflow your team already uses.
FRAGGLEdrive™ makes your data unreadable to attackers — it protects it at all times, even after it's stolen.
Financial statements, legal and client files, mergers & acquisitions (M&A) documents, court records, PII, PHI/EHR, and patient charts — they all move across laptops, vendor portals, and cloud drives every day. Each destination is a place where encryption can quietly stop.
Financial statements, legal and client files, patient charts, grid schematics, game assets, gaming-floor records — they all move across laptops, vendor portals, and cloud drives every day. Each destination is a place where encryption can quietly stop.
of attacks now use AI to locate and exfiltrate data, and increasingly target small and mid-size organizations.
AI has compressed breach timelines from days to minutes, leaving far less time to detect and respond.
faster data exfiltration once an attacker is inside, accelerating theft, extortion, and dark-web resale.
Sources: industry threat research, 2025–26.
A patchwork of mandates. GLBA and NYDFS govern financial data; HIPAA governs healthcare records; NERC CIP governs utility and grid systems — each requires demonstrable encryption, not just a policy statement.
Double extortion. Ransomware actors increasingly exfiltrate files before encrypting them, threatening publication or fraud unless the organization pays. Encrypted, fragmented data has nothing usable to leak, sell, or extort.
A departing employee, a lost laptop, or a mis-shared folder shouldn't be able to expose a client roster, a source repository, or a patient or client record on its own.
Vendors, contractors, and outside partners all touch the same files. One under-secured endpoint anywhere in that chain can expose data that was never the original target.
Most encryption protects data in transit and at rest but leaves it fully readable the moment it's decrypted for use. Fragmentation keeps individual pieces meaningless even then.
Watch it encrypt your data, scatter fragments across five storage locations, and see what a hacker would see.
Counterparty: Meridian Holdings LLC
Purchase price: $48,500,000
Escrow account: 8841-4471-2290
Close date: 2026-11-14
FRAGGLEdrive™ installs, operates, and appears as a standard disk drive on your Windows PC or laptop, so you save files the usual way. While you work, encryption and fragmentation happen automatically in the background on the endpoint, with data stored as secure, encrypted fragments.
Save a file to FRAGGLEdrive™ the same way you'd save to any drive. No new export step, no retraining or learning, no change to the workflow your team already uses.
CYBERVORE's patented FRAGGLEstorm™ engine encrypts the file using NIST AES-256 encryption, then splits it into individually meaningless pieces — no patterns, descriptions, or metadata — so a single fragment, or even several, is meaningless without authorization.
Encrypted fragments are distributed across one or more storage destinations you already control — on-premises servers and storage, OneDrive, Box, Dropbox, Google Drive, and any S3-compatible storage such as AWS and Wasabi — all tailored to your residency and infrastructure requirements. Seventy (70) cloud storage vendors are directly supported, with the Amazon S3 protocol available for any service that supports it.
Only authenticated users can retrieve encrypted fragments and reassemble them into the original file. When an employee is offboarded or loses a device, the FRAGGLEdrive™ and its associated fragments become immediately inaccessible.
CYBERVORE doesn't host your files and doesn't sell storage. Your organization decides exactly where encrypted fragment data resides, which keeps compliance commitments demonstrable rather than aspirational.
FRAGGLEdrive™ layers on top of storage you already have. No new hardware, no forklift migration, no application changes, no dedicated appliance to rack and maintain.
FRAGGLEdrive™ uses your existing identity and access management (IAM) system via Okta or Auth0, with industry-accepted secure authentication such as multi-factor authentication (MFA). The same credentials that govern your core platform also govern the drive.
Offboard an employee, close an account, or respond to a lost device by switching the user off. Access ends immediately, audit trail intact.
CYBERVORE licenses FRAGGLEdrive™ software per device, but a single license can support multiple drives — run separate drives for different teams, projects, personal or business use, or classification levels on one workstation, each with its own storage map and access policy.
Security buyers don't take a vendor's word for it, and they shouldn't have to. FRAGGLEdrive™ is backed by independent analyst reviews and third-party testing.
Jack Poller, Principal Analyst with 30-plus years of industry experience
“FRAGGLEdrive is a highly secure, incredibly cost-effective, and transparent approach to data defense that every growing business needs…”
January 2026
Dr. Edward Amoroso, CEO, TAG, Research Professor, NYU Carlier Hernandez, Research Associate, TAG Data Research Team
“FRAGGLEdrive is exactly the kind of invisible, multi-layered data protection that high-risk organizations need to safeguard critical files from advanced adversaries.”
May 2025
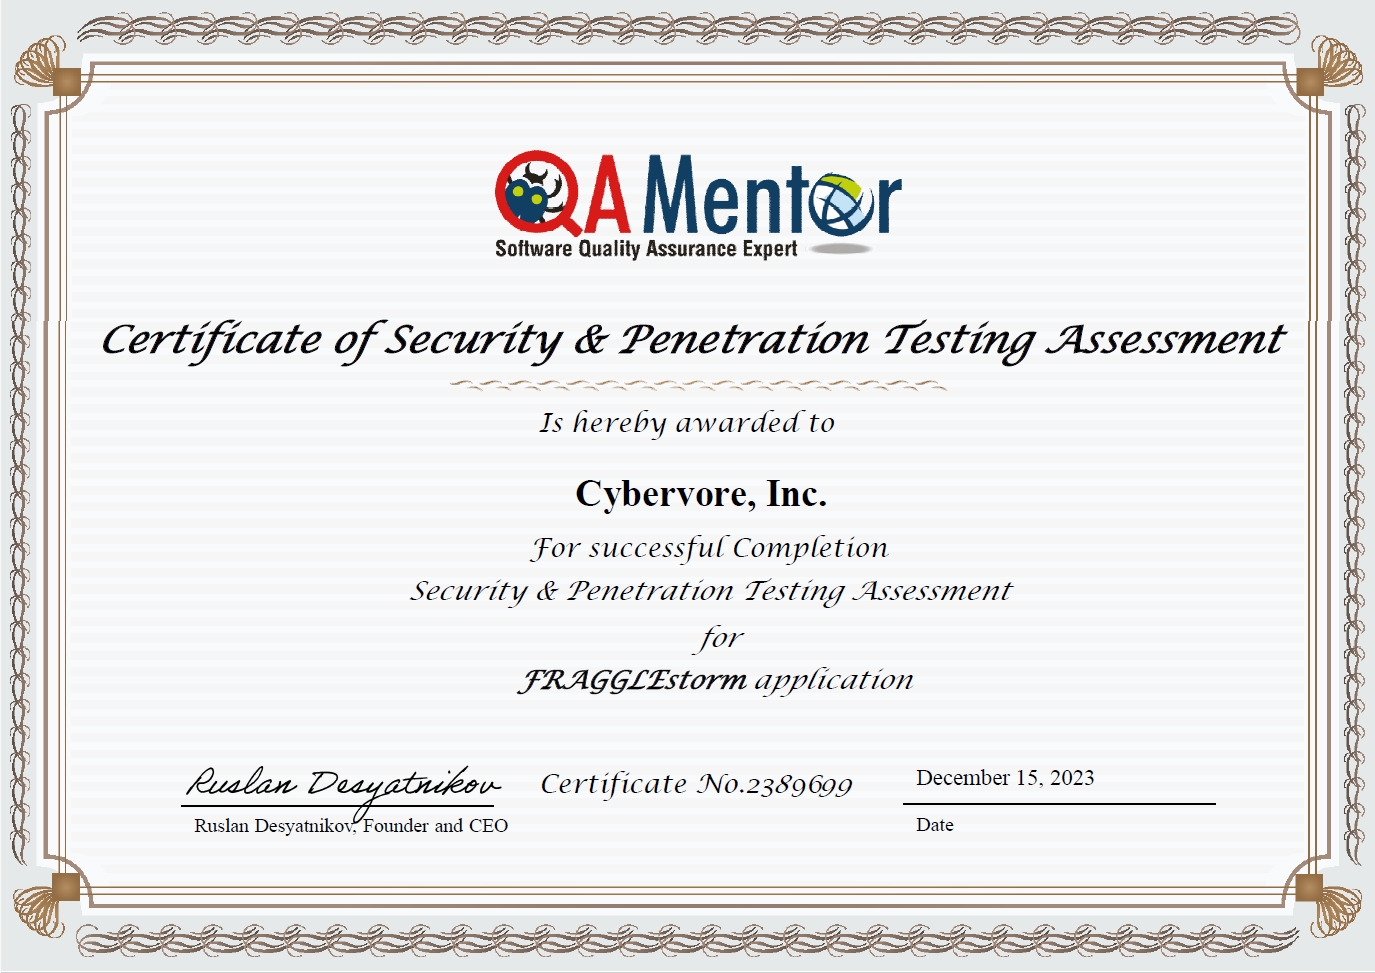
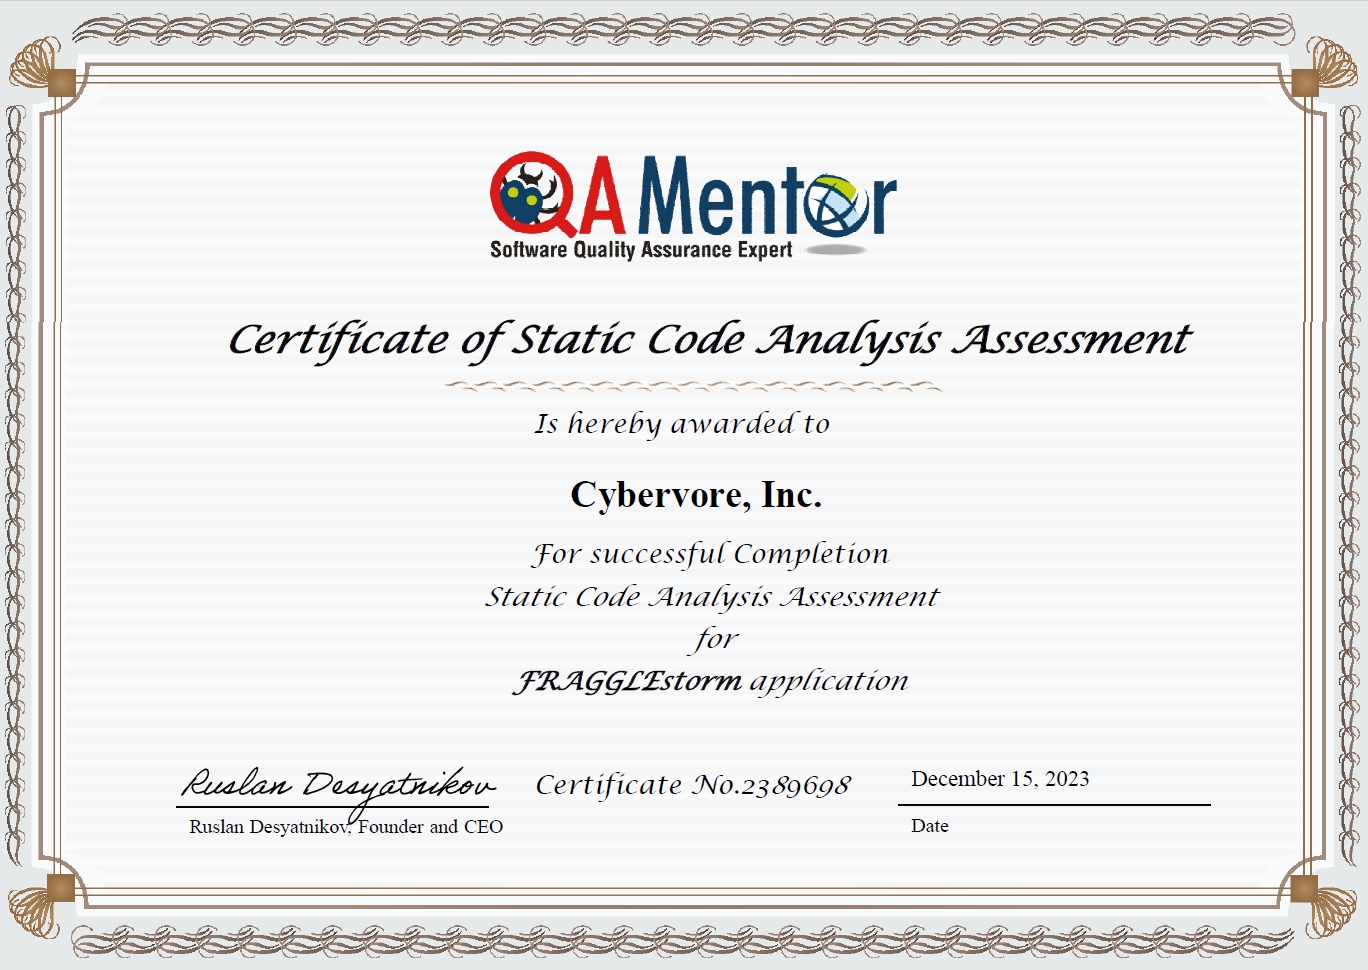
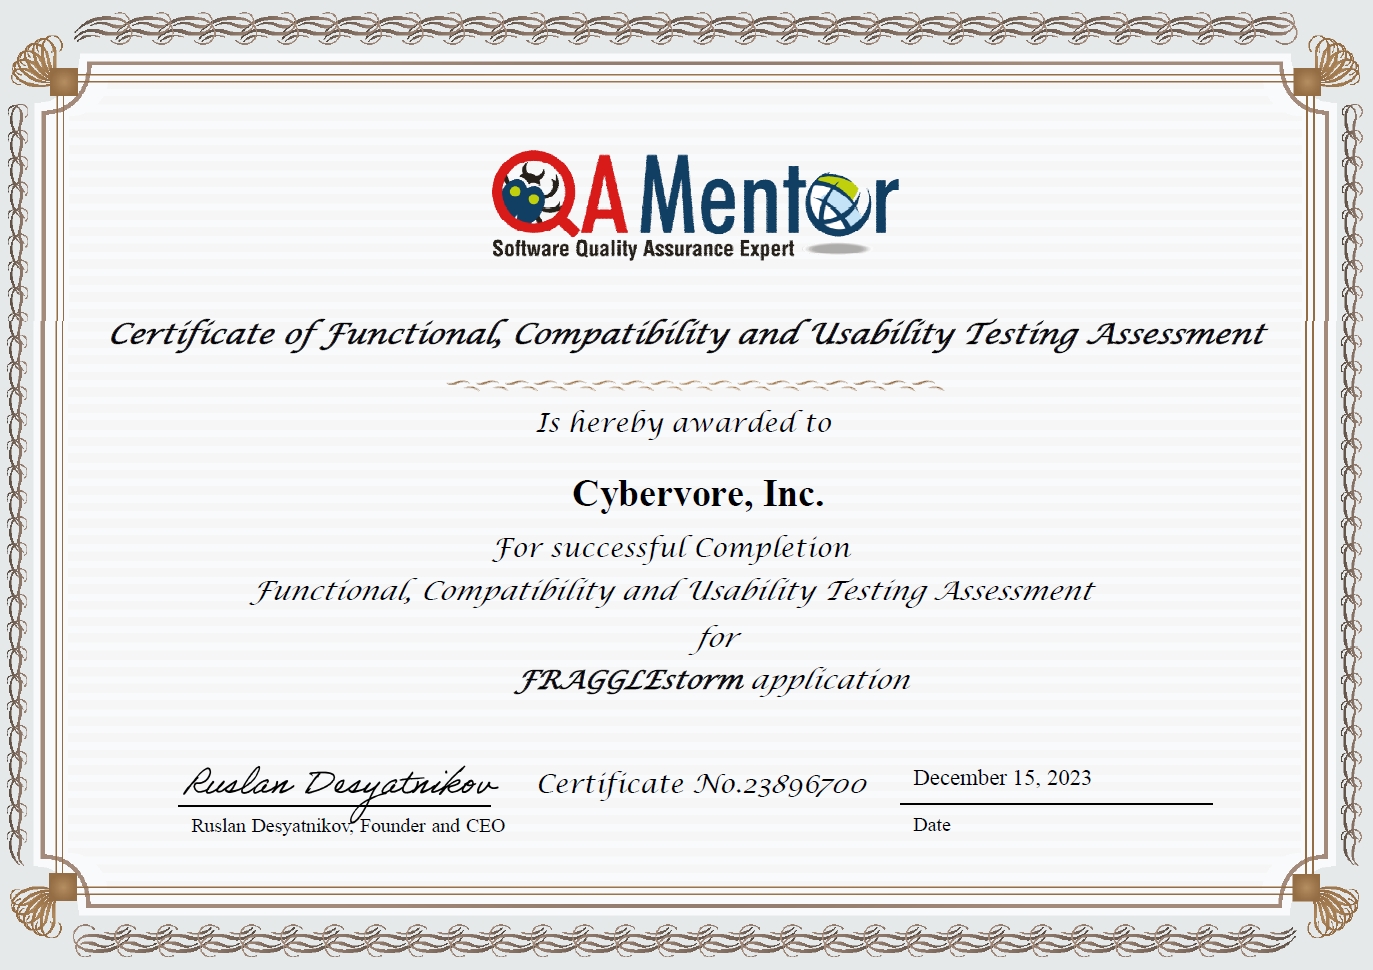
Ruslan Desyatnikov, CEO, President, and Founder – Over 22 years of Quality Assurance, Quality Control, Process Improvement, and software testing. Tests performed - Independent functional, penetration, and static-code testing Completed, validated, and awarded certificates
December 2023; see below
Security Penetration Testing Certificate
Functional Testing Certificate
Static Code Analysis Certificate
NIST FIPS 197 Advanced Encryption Standard
Architecture: Fragglestorm™ is built to a Zero Trust-aligned model
Three regulated verticals, one endpoint. Each solution page maps the drive to the specific mandate and threat model that the vertical addresses.
Privileged filings and case files move securely between attorneys, courts, and clients without becoming readable if a single device is compromised.
Account numbers, wire instructions, and statements are what attackers monetize first. Fragmentation keeps them unreadable end-to-end — supporting GLBA, NYDFS, and Reg S-P commitments.
A single exposed chart can trigger a breach notification and an investigation. Patient and clinical files are fragmented at the endpoint, keeping PHI unusable outside an authenticated care workflow — aiding HIPAA compliance.
Hardened, certified, commercially supported endpoint disk drive.
Shared FRAGGLEdrives with multi-user access roles, data resiliency plus data loss and ransomware discovery and recovery, and generative AI customer support and services.
Server and cloud management, central policy, key custody, and monitoring. Agentic AI performance monitoring, discovery, configuration, and customer setup.
Agent-based scale, compliance, e-discovery, and multi-tenant delivery - AI enabled. Distributed server and cloud management. Central policy, key custody, and performance monitoring and balancing.
Install FRAGGLEdrive™ in minutes, map your first drive's storage, and see what an unreadable breach looks like — at no cost for 30 days.